Client project
Industry: Financial Services
Managed SOC for a Financial Services Firm
- SIEM
- Wazuh
- EDR
- Firewall
- Threat Intelligence
Delivery duration: Defined after discovery; no verified delivery record published.
Overview
A mid-sized financial services company needed round-the-clock visibility over its network after a near-miss phishing incident exposed how blind its team was to active threats.
The Challenge
Alerts were scattered across disconnected tools, no one was watching outside business hours, and the security team could not tell a real attack from routine noise. A single missed alert could mean a regulatory breach.
The Solution
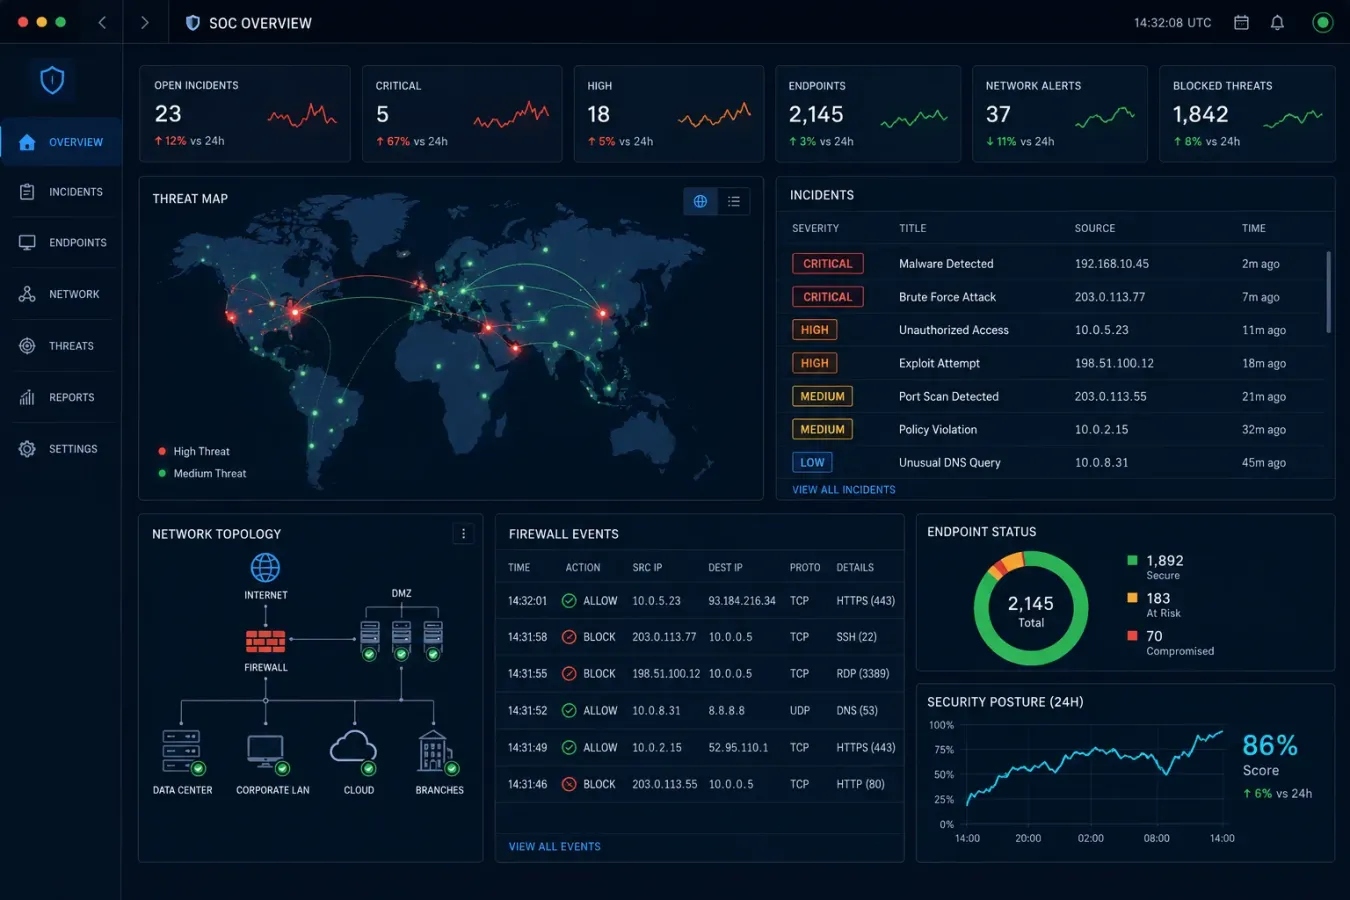
We deployed a centralized SIEM, onboarded every critical log source, and built tuned detection rules mapped to the threats that matter for finance. Our analysts took over 24/7 monitoring with a defined escalation and response playbook.
How we verify success
Before implementation, we agree on a baseline and acceptance criteria. Performance, security checks, recovery tests, and operational handover are documented against that baseline. No improvement figure is claimed here without a verified measurement.
Gallery