Client project
Industry: Server Fleet Management Software
Dinosoft Fleet Console: A Server Console That Can Never Push Code
- PowerShell 5.1
- Laravel 13
- Filament
- PostgreSQL 18
- PHP 8.4
- Docker Compose
- nginx
- DPAPI
Delivery duration: Defined after discovery; no verified delivery record published.
Overview
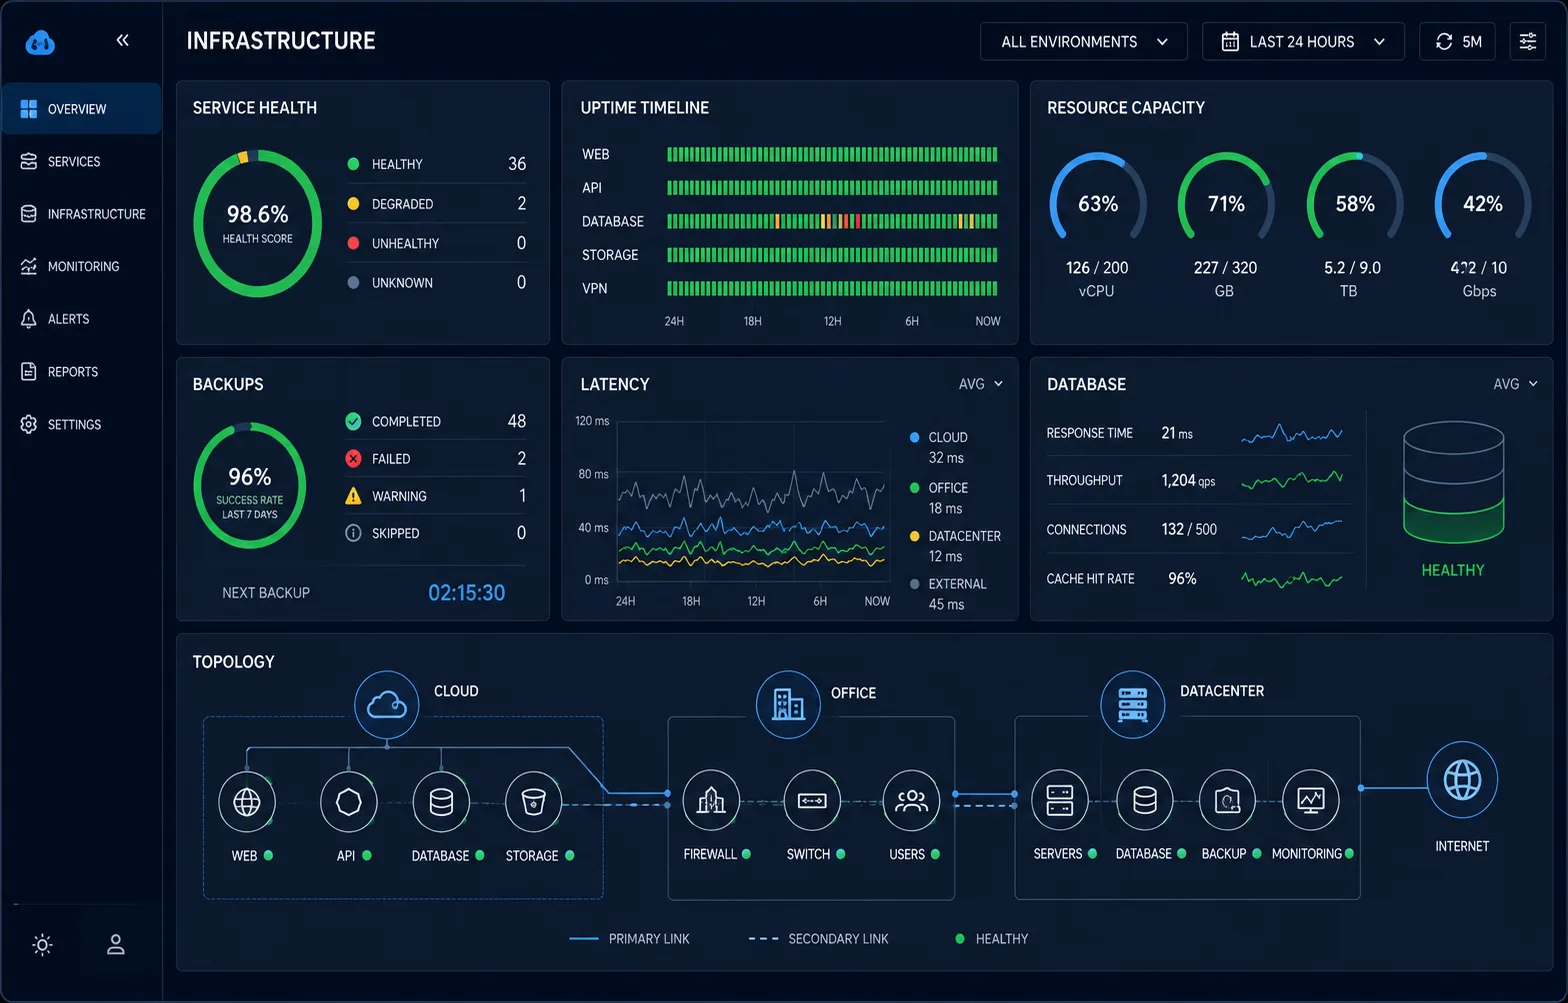
Dinosoft Fleet Console is a DinoSoft product for managing Windows servers that run business applications and SQL Server. It reports each server's status, verifies backups, archives folders, runs destructive commands such as file deletion only after approval, and updates its own agents. It is built and tested, but it has not yet been put into service on live servers.
The Challenge
A console that can reach every server is exactly what an attacker wants. If it can send code, one breach of the console becomes a breach of every server it manages. Maintenance jobs such as deleting files are destructive by nature, and asking staff to be careful is an intention, not a control. Managing the servers also could not mean opening an inbound port on any of them, and the agent could not require a new runtime to be installed on them.
The Solution
We built the agent in Windows PowerShell 5.1 so that it needs no new runtime on the servers. It only pulls work: it makes outbound HTTPS requests and never listens on a port. The console can only issue commands from a closed list with validated parameters, so it can never push code. Destructive commands run in two phases: first a plan, then an approval tied to that plan's hash. The agent refuses to run if the server no longer matches what was approved. Each agent's private key is protected with machine-scope DPAPI and never leaves its server, so even a compromised console cannot impersonate an agent. Security settings, such as where deletion is allowed and which restart command runs, are set locally on each server and can never be changed remotely. Agent updates must be signed with an offline key that is not on the console, so a breached console can queue an update but cannot forge one. The test suite got the same scrutiny. It had been wiping the application's main database instead of its test database on every run, admin account included, while every test stayed green. The cause was a Docker Compose environment variable that hid the test configuration, because Laravel's environment loader never overwrites a variable that is already set. A guard now refuses any database whose name does not end in _test.
How we verify success
Before implementation, we agree on a baseline and acceptance criteria. Performance, security checks, recovery tests, and operational handover are documented against that baseline. No improvement figure is claimed here without a verified measurement.